A public, searchable dump naming over 41,000 Homeland Security workers puts frontline agents and their families at risk.
Story Highlights
- An activist-linked site posted a database tied to more than 41,000 Homeland Security personnel
- Records include names, offices, work contacts, and assignments across multiple components
- Department of Homeland Security confirmed it is addressing a potential breach
- Hackers claimed access through the department’s single sign-on provider, Okta
What Happened: A Massive Personnel Exposure Went Public
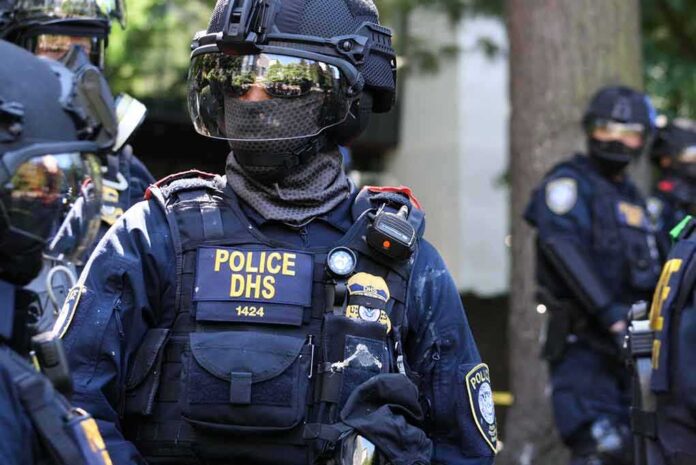
Reporters at the Washington Post and CNBC said an activist group released a searchable database listing more than 41,000 people tied to the Department of Homeland Security. The list spans Immigration and Customs Enforcement, Customs and Border Protection, citizenship services, and department headquarters. Some entries point to investigative or undercover roles. The release moved beyond social posts because a leak platform hosted the files, and a separate site mirrored them for search access.
The material reportedly included names, offices, work emails, phone numbers, job titles, and assignments. That set of details can map how teams work and who does what. It can also help people target specific officers. The Department of Peace, the name used by the hackers, said they pulled the data through Okta, a single sign-on service. Reporters have not independently proven that technical claim, but the group put its name on it.
What Officials Confirmed—and What Remains Unclear
The Department of Homeland Security said it is aware of a potential breach and is working the case. Officials said they are taking steps to protect employees as the probe continues. That statement confirms a real incident, even if all details are not final. Reporters also noted the database itself warned it is not a complete directory and might include inaccuracies, which means the exact count and freshness of entries are not settled.
Coverage emphasized that some of the exposed roles appear sensitive. That concern drove quick calls to remove mirrored sites and to contact hosting firms. One report described a takedown request that framed the database as doxxing rather than whistleblowing. That framing matters because it centers safety and privacy for officers, not the hackers’ politics. It also limits outside review of the raw files, which slows public verification of claims.
Why This Matters to Border Security and Public Safety
Border and immigration officers already face threats at home and on the job. Publishing a roster tied to assignments gives agitators a roadmap. It can help cartels, traffickers, and violent activists identify people to pressure or harm. Even if most entries show only work contacts, hostile actors can connect dots fast. A breach like this also signals to other bad actors that targeting law enforcement rosters is possible and profitable for intimidation or disruption.
The activist group behind an apparent data breach at the DHS appears to have targeted officials connected to the department's immigration & border enforcement operations. https://t.co/uO2PCL6HuS
— The National Desk (@TND) October 30, 2026
The reported Okta angle fits a wider pattern in recent breach data. Major industry reporting found stolen passwords and abuse of identity tools drive a large share of break-ins. Single sign-on helps users, but it also creates a rich target when criminals hijack accounts. That is why stricter checks, fast device signals, hardware keys, and tight access rules are essential. Agencies must expect that activists and foreign actors will probe identity systems every day.
What the Trump Administration Should Do Next
President Trump’s team should surge help to the department’s cyber unit and to every affected component. First, lock down access: require hardware security keys for all personnel with elevated roles, and reset tokens where any doubt exists. Second, push rapid alerts and safety checks for officers in sensitive posts. Third, publish a de-duplicated count, by component, that avoids exposing new data but confirms scope to Congress and the public. Transparency builds trust and deters rumor.
Congress should back targeted funds for identity defense, not bloated tech projects. Tie money to clear results: phishing-resistant logins, device checks, and faster incident response. Demand timelines for the department’s inspector general review and for a lessons-learned report. If the hackers’ Okta claim proves true, require stronger vendor standards and real penalties for sloppy controls. Protecting officers and stopping doxxing is not optional—it safeguards the rule of law and the communities those officers serve.
The Bottom Line for Readers
Homeland Security employees and contractors now face higher risks because a large roster went online. The department confirmed a real incident and is taking action. The exact size and the hacker’s full method remain under review. But the mission is clear: shield the people who enforce our laws, fix identity weaknesses fast, and ensure that political activists cannot endanger families by dumping work rosters on the web. Safety and strong borders depend on it.
Sources:
facebook.com, washingtonpost.com, wtsp.com, endtimeheadlines.org, cbc.ca, ibtimes.co.uk